The most consequential shift in cyber risk is no longer about stolen data; it is about adversaries reaching through networks to manipulate the physical world—now including the temperatures that keep food, medicines, and blood products safe.
At a Glance
- Five U.S. federal agencies warned of ongoing malicious activity targeting industrial refrigeration and cold-chain monitoring systems worldwide.
- Exposed and unpatched temperature controllers—often left online with default credentials—are the primary footholds for attackers.
- Successful compromise can alter temperatures and trigger real hazards: inventory loss, equipment damage, and even fire risk.
- The threat spans healthcare, food and agriculture, chemical facilities, and transportation—anywhere cold-chain reliability is mission-critical.
- Recent European incidents and a specific FBI account of attempted disruption at French blood facilities underscore the risk in practice, not theory.
What the Government Warning Actually Says—and Why It Matters
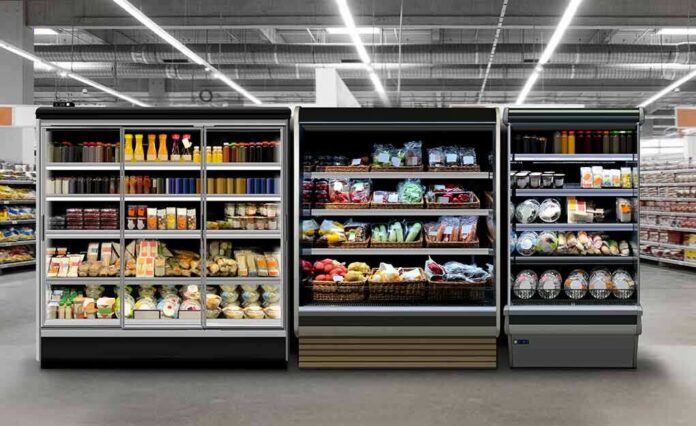
On November 5, a coalition of U.S. agencies—CISA, the FBI, HHS, USDA, and DOT—issued a joint advisory stating they are aware of malicious cyber activity targeting industrial refrigeration and cold-chain monitoring systems globally. This is not a generic “be vigilant” missive. The alert names concrete exposure conditions, including unpatched or internet-accessible electronic temperature controllers and commercial refrigeration controllers, and prescribes immediate steps: remove unnecessary public internet access, change vendor-default passwords, apply updates, and isolate operational technology (OT) networks from IT and the public internet. The specificity is the point. Temperature controllers are small, inexpensive, and widely deployed—yet when reachable over the internet with factory-set credentials, they become high-leverage instruments for adversaries.
The advisory also sets out the stakes. If attackers gain access, they can adjust temperatures, disable alarms, or force destructive cycles—creating fire hazards, reducing service life, and spoiling inventory. In the cold chain, where products have narrow thermal tolerances, such manipulation can turn an hour of unauthorized access into a costly and potentially dangerous event.
From Screens to Shelves: How Attacks on Controllers Become Physical Damage
Mechanically, the path looks like this: an attacker finds internet-facing refrigeration controllers using scanning tools; default or weak credentials provide entry; the interface then permits legitimate functions—setpoint changes, defrost cycles, alarm suppression—to be misused. Because many such devices were designed for convenience (remote monitoring, vendor service access) rather than adversarial resilience, they often lack multifactor authentication or robust logging. Once inside, an attacker does not need exotic malware; the built-in controls suffice to raise a freezer from -18°C to ambient or higher, thawing stock and stressing compressors. The joint advisory describes exactly these weaknesses and urges segmentation so that even if an enterprise IT account is compromised, an intruder cannot pivot unimpeded into OT.
The consequence profile is broad. In food retail, it means spoiled meat and produce; in healthcare, degradation of vaccines, temperature-sensitive medications, and samples; in blood services, induced risk to plasma and whole blood reserves. CISA’s plain warning—altered temperatures can cause fire hazards, inventory loss, and reduced equipment life—reflects direct experience with how thermal cycles, load, and compressor duty interact under abnormal setpoints or forced defrost.
Evidence From the Field: European Incidents and a Blood-Service Case
Independent reporting aligns with the advisory. Outlets have detailed incidents in European supermarkets where remote access led to abnormal temperature changes and spoilage, and French officials acknowledged targeting of refrigeration at several blood-bank sites. In parallel, the FBI released a video advisory describing an attempted disruption at three French national blood-service facilities, stating that attackers gained access via controllers that were unpatched, internet-reachable, or still using default passwords listed by manufacturers. These accounts reinforce the advisory’s central claim: attackers are not merely probing; they are manipulating real systems when conditions allow.
Attribution remains intentionally absent from the joint warning—no specific group or state actor is named. That restraint is unsurprising: incident responders often separate urgent defensive guidance (how to harden now) from slower, more sensitive questions of perpetrator identity. What matters for operators is that the intrusion pathway is well understood and broadly fixable: remove direct internet exposure, change defaults, update firmware, segment networks, and enforce strong authentication.
Why Cold-Chain OT Became a Target
Cold-chain control has all the characteristics adversaries prize: ubiquity across sectors, operational criticality, and an installed base that is highly heterogeneous—new units alongside legacy devices no longer receiving vendor support. Many controllers sit in facilities where capital budgets and downtime windows are tight; upgrades lag, network diagrams are stale, and integrators have chained convenience features that seemed harmless at deployment. The result is an attack surface distributed across grocery backrooms, hospital pharmacies, food processors, and transportation depots. Fragmented ownership exacerbates the problem: responsibilities split among operators, OEMs, and service contractors dilute accountability for patching and credential hygiene, which the advisory explicitly addresses.
Context from the broader OT threat landscape is instructive. Across industry, ransomware and extortion dominate incident counts, yet most cases do not involve direct manipulation of industrial controls; operators shut down processes as a precaution or due to IT disruption. That baseline makes deliberate setpoint tampering in refrigeration notable—it crosses from business interruption into engineered physical effect, with comparatively simple means. The joint advisory’s sector list—Healthcare and Public Health, Chemical, Food and Agriculture, and Transportation Systems—maps precisely to the domains where a few hours of thermal drift can destroy high-value inventory or disrupt essential services.
Practical Defense: What Works, What Fails, and What to Tackle First
Defensive priorities follow the failure modes the government named. First, eradicate unnecessary internet exposure: controllers and their management portals should sit behind VPNs or zero-trust gateways, not on public IP space. Second, change all default passwords and disable vendor backdoor accounts where possible; implement multifactor authentication for remote access. Third, patch and update firmware; where devices are end-of-support, plan replacement rather than indefinite life extension. Fourth, segment OT from IT with firewalled conduits and strict allowlists; a single flat network is an attacker’s best friend. Finally, tighten alarm management: require cross-channel alerts (local HMI, email/SMS, and out-of-band) for out-of-range temperatures and configuration changes, and enforce “two-person” confirmation for critical setpoint edits during remote sessions.
Operators should also inventory controllers at model and firmware granularity, document who can access them (including contractors), and test rollback procedures after malicious or accidental setpoint changes. In healthcare and blood services, integrate cybersecurity with Good Distribution Practice and USP storage standards: treat remote access pathways as quality-critical infrastructure. In food retail and logistics, tie cybersecurity controls to HACCP plans so that network changes are assessed for their impact on temperature assurance. The agencies’ guidance is clear; the execution must align with the operational realities of busy facilities where maintenance windows are scarce.
CISA, the FBI, HHS, USDA, and the Department of Transportation issued a joint warning on November 5 about ongoing cyberattacks targeting industrial refrigeration and cold-chain monitoring systems.
The alert follows a wave of attacks across Europe.Hackers remotely accessed…
— Keith Ainsworth (@AinsworthKeith) November 8, 2026
What to Watch Next
Expect continued emphasis from federal partners on eliminating default credentials and public exposure, alongside targeted outreach to the sectors named in the advisory. Given the breadth of the installed base, remediation will be uneven; organizations with strong vendor management and asset inventories will move fastest. The near-term risk is not exotic malware but ordinary misconfiguration exploited at scale. The medium-term risk is adversaries chaining access across sites—learning once, applying many times—until defenders close the obvious doors. The joint warning gives operators a straightforward checklist; the outcome now hinges on disciplined execution and sustained attention to OT fundamentals.
Sources:
thehill.com, cisa.gov, bleepingcomputer.com, cbsnews.com, scworld.com, dragos.com